Page
Agent DLP™ + NVIDIA OpenShell
Agent DLP for NVIDIA OpenShell
Bedrock Data brings enterprise data context to every agent action in NVIDIA OpenShell, part of the NVIDIA Open Agent Safety Platform. Agent DLP evaluates each agent action against your data policies, and OpenShell enforces the decision before the action takes effect.
NVIDIA OpenShell sandbox
Click a highlighted call to see its Agent DLP decision
>
Bedrock Data
Agent DLPwaiting
Agent DLPwaiting
Action
…
Data
…
Destination
…
WAITINGNo outbound action yet
Bedrock Data Policyevaluates the payload
Illustrative replay. Names and records are fictional.
Agent DLP use cases: PHI and proprietary code in OpenShell
Healthcare · PHI
Keep patient data in HIPAA-compliant environments
Agentic debugging and everyday company workflows can't move PHI outside sanctioned environments, even when the agent holds every permission the job needs.
Software · Intellectual property
Keep proprietary code inside the company
Agents can share open source code freely while your own code stays out of public issues and repositories. Bedrock Data knows which code is yours and where it may be shared.
THE PROBLEM
Why least privilege doesn't keep AI agent data safe
Every permission can be correct, yet data can still leak.
- PROMPTT+00:00
A debugging task comes in
An engineer asks the agent why last night's claims_sync job failed.
✓ Expected work - DATA ACCESST+00:41
The agent opens the patient database
It needs real records to find the bad row. Access is justified for debugging.
Permission✓ Passed access reviewSELECT on claims_db.patients - ROOT CAUSET+03:12
It finds the root cause
Its investigation skill says to report findings to the incident channel.
Permission✓ Passed access reviewchat:write on #eng-incidents - DATA LEAKT+03:15
Patient data lands in Slack
The report carries the patient record it found, and the whole channel can read it.
✕ Data leaked
Enterprises are running fleets of long-horizon agents that fan out into thousands of sub-agents, and permissions alone can't tell them which data can safely move where. NVIDIA OpenShell enforces policy on every agent action at the sandbox boundary. Bedrock Data's supervisor middleware makes that decision data-aware, so the runtime that isolates the agent also knows what the agent is carrying.
Where Agent DLP runs
Where Agent DLP runs: from the agent gateway to the OpenShell sandbox
Agent DLP already inspects agent traffic at the gateway. Inside NVIDIA OpenShell, it evaluates every action that leaves the agent’s sandbox, whether the agent uses an MCP tool, runs a command or writes its own code.
At the gateway
Tool calls between agents and MCP servers
AWS AgentCoreLiteLLM
- Every request an agent sends to an MCP tool
- Every response the tool sends back
- Allow, redact or block on each call
In the sandbox
Every action that leaves an OpenShell sandbox
 OpenShell
- MCP tool calls
- Command-line invocations
- Code the agent writes itself
HOW IT WORKS
How Agent DLP works with OpenShell Supervisor Middleware
01
Agent in NVIDIA OpenShellThe agent issues a call
A tool call, command or message heads out of the sandbox. OpenShell authorizes it against sandbox policy first.
02
Supervisor Middleware · Bedrock DataThe middleware consults Bedrock Data
Bedrock Data plugs into OpenShell’s Supervisor Middleware. At the enforcement point, the middleware sends each request to Bedrock Data, which checks what the data is, who can access it and where it’s headed, using classification already built in place across your environment.
03
NVIDIA OpenShellApproved or rejected
Approved calls go through. Rejected calls stop before they take effect, and the agent gets a path to revise.
WHAT BEDROCK DATA ADDS TO OPENSHELL
What Bedrock Data adds to NVIDIA OpenShell
Runtime
A decision on every authorized request
Each request gets a go or no-go based on what the data is and where it's going.
Design time
An agent's blast radius before it runs
Security teams see the data an agent can actually reach, the toxic combinations it can create and where policy would be violated.
Data-aware
Enforcement that keeps up with your data
As data and access change, the decisions OpenShell enforces change with them, and nobody rewrites a rule.
ROLLOUT
How to roll out Agent DLP in OpenShell: observe, then enforce
01
Connect
Add Bedrock Data to OpenShell's Supervisor Middleware. Your agents and their tools stay as they are.
02
Observe the policy
In observe-only mode, Agent DLP returns a decision on every action without enforcing it, so you see what the policy would have done.
03
Enforce once validated
When the policy behaves the way you expect, switch it to enforcement and OpenShell acts on every decision.
Frequently Asked Questions
Related Resources
Blog
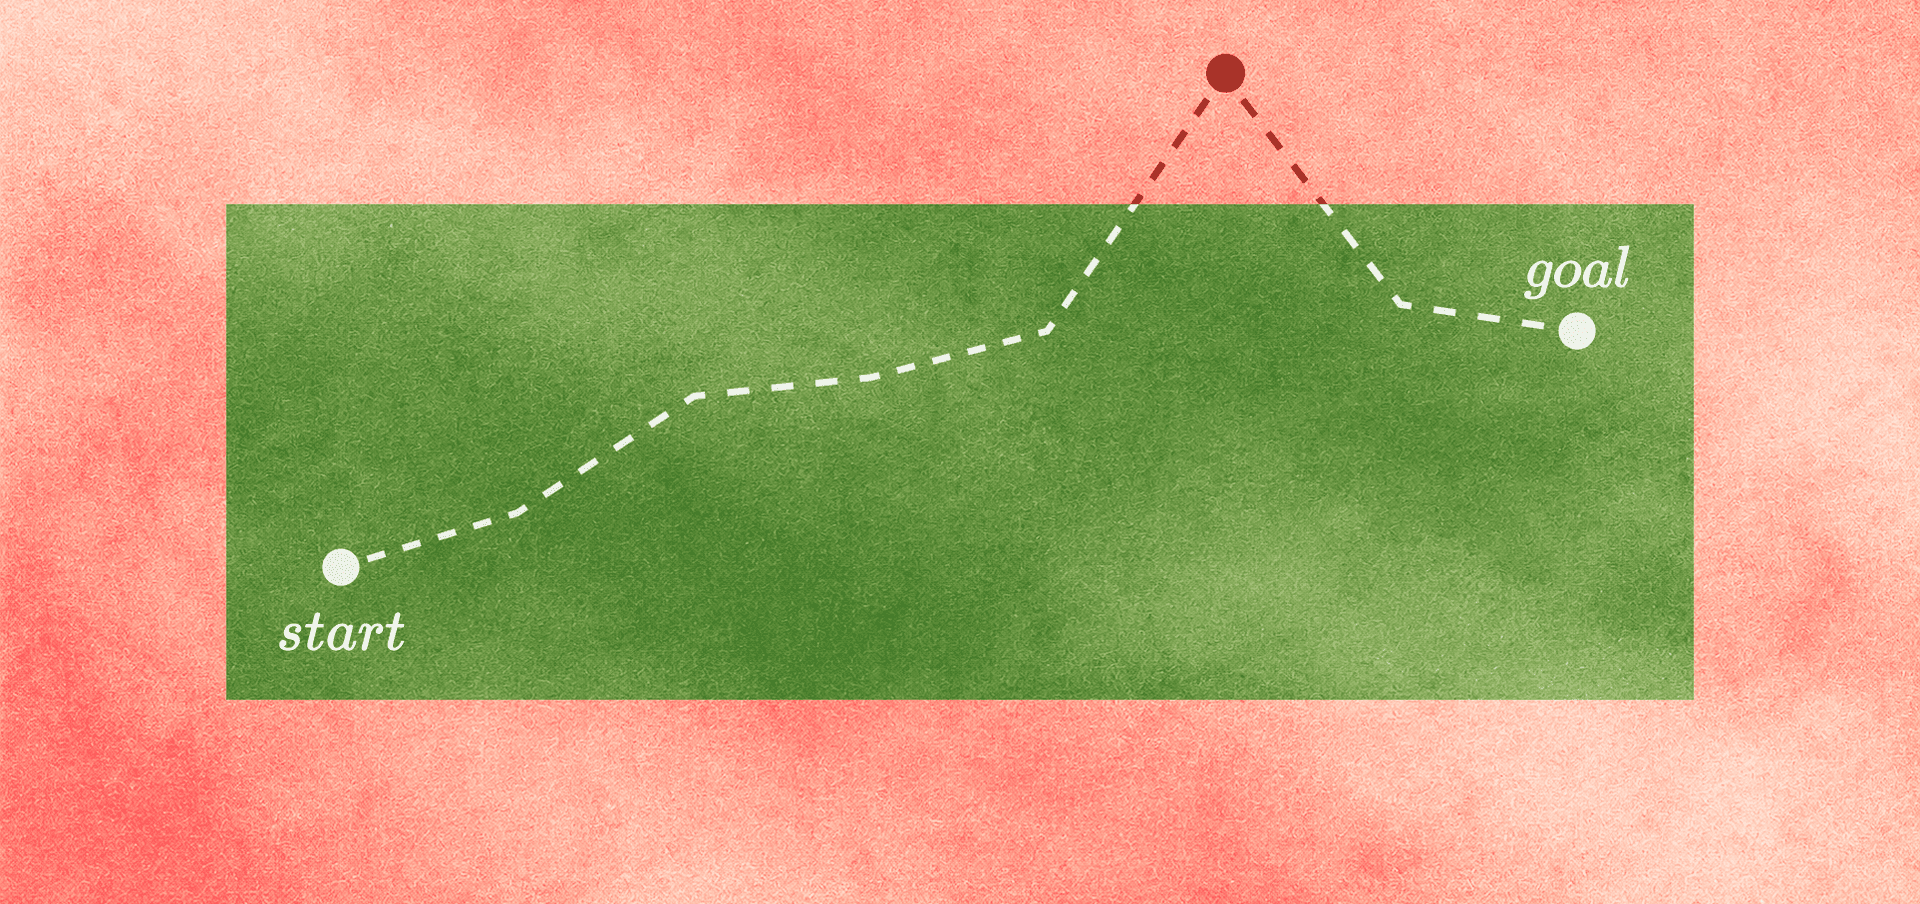
Least privilege is not least risk: data-aware sandboxes for AI agents
Sep 28, 2026
News
Bedrock Data Integrates With NVIDIA OpenShell to Bring Data-Aware Policy Enforcement to AI Agents
Sep 28, 2026Page
Agent DLP
Blog
Watching the Agent's Hands: Governing AI Agent Tool Calls with Bedrock Data’s Agent DLP
Jul 30, 2026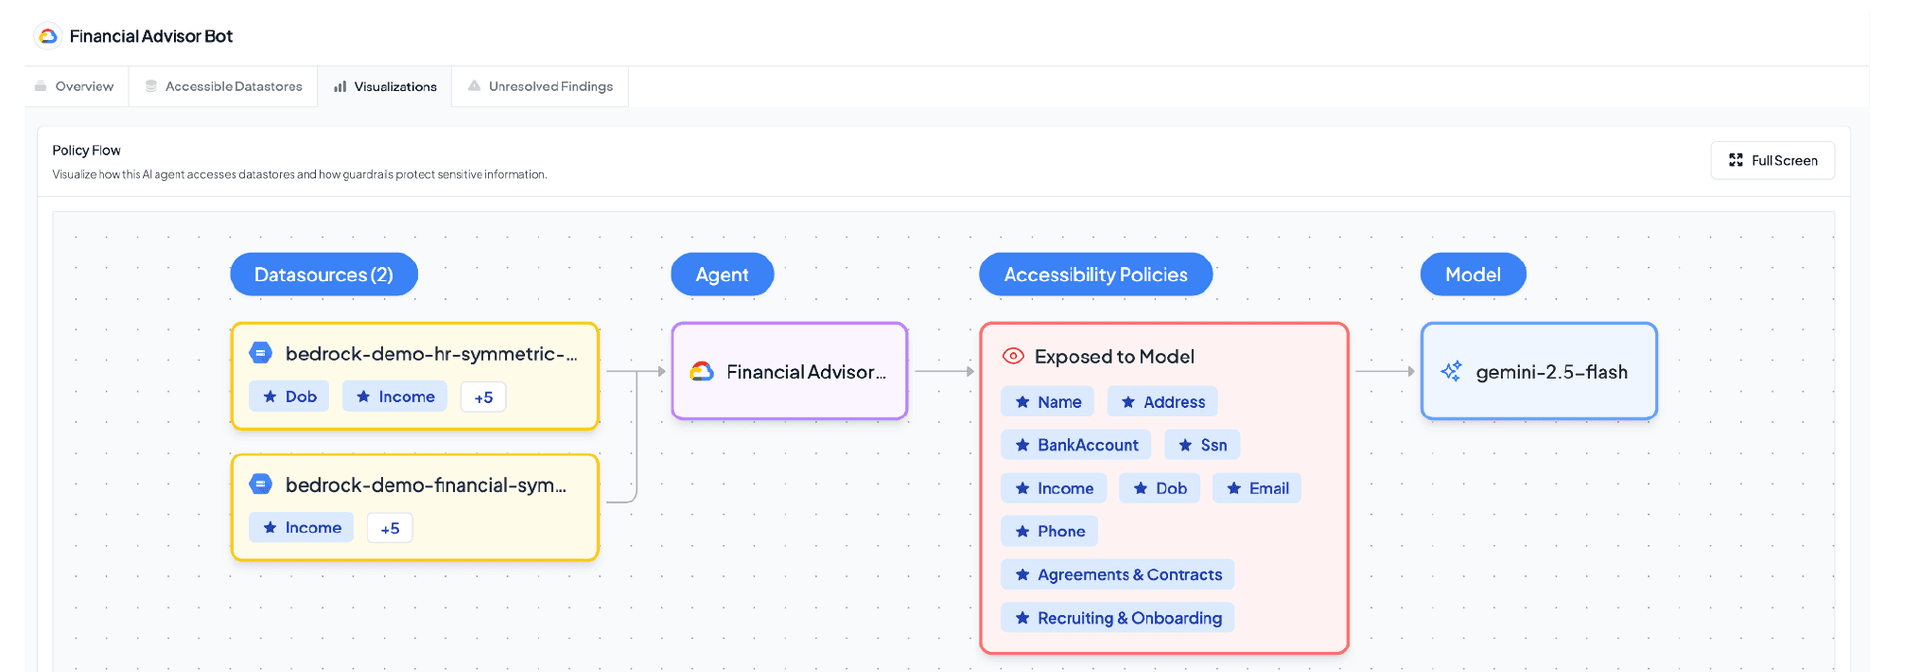
Blog