datastores reachable by the median OAuth app or service account
- App / agent identity
- 55
- Median employee
- 3–4
ArgusAI · Agent DLP
Runtime data loss prevention built for AI agents. Agent DLP sits inline at your agent gateway, inspects every tool call in both directions, and enforces your policies the moment data moves.
Trusted by security teams at


| Time | Agent | Tool call | Request & response | Action |
|---|
datastores reachable by the median OAuth app or service account
Secrets
of apps that can reach data can reach stored secrets such as API keys and tokens
Sensitive by default
of identities that can reach any data can reach sensitive data
Classification
bytes scanned carries a sensitive classification. Most of it is financial, security and confidential business data.
Blast radius
datastores, roughly 21 PB, reachable by a single identity in one environment
Gartner projection
of unauthorized AI transactions through 2026 will come from internal policy violations rather than external attacks, Gartner projects.
About the study
Anonymized Bedrock Data telemetry across 70+ PB, ~180,000 datastores and 40,000+ identities in technology, finance and healthcare.
An agent wired to tools pulls full customer records autonomously, at machine speed, with no human in the loop. Every existing control layer sits somewhere else.
Control | What it sees | Sees the tool call? |
|---|---|---|
Network and access controls | Whether a tool can reach a datastore | No |
Storage-layer data protection | Data at rest, and reads against a system | No |
Model-side guardrails | The prompt and the model response | No |
Traditional DLP | Employees moving files across email, endpoints and cloud apps | No |
Agent DLP | Every request an agent sends to a tool and every response it gets back, with the identity and policy behind it | Yes |
Network and access controls
What it sees
Whether a tool can reach a datastore
Sees the tool call?
Storage-layer data protection
What it sees
Data at rest, and reads against a system
Sees the tool call?
Model-side guardrails
What it sees
The prompt and the model response
Sees the tool call?
Traditional DLP
What it sees
Employees moving files across email, endpoints and cloud apps
Sees the tool call?
Agent DLP
What it sees
Every request an agent sends to a tool and every response it gets back, with the identity and policy behind it
Sees the tool call?
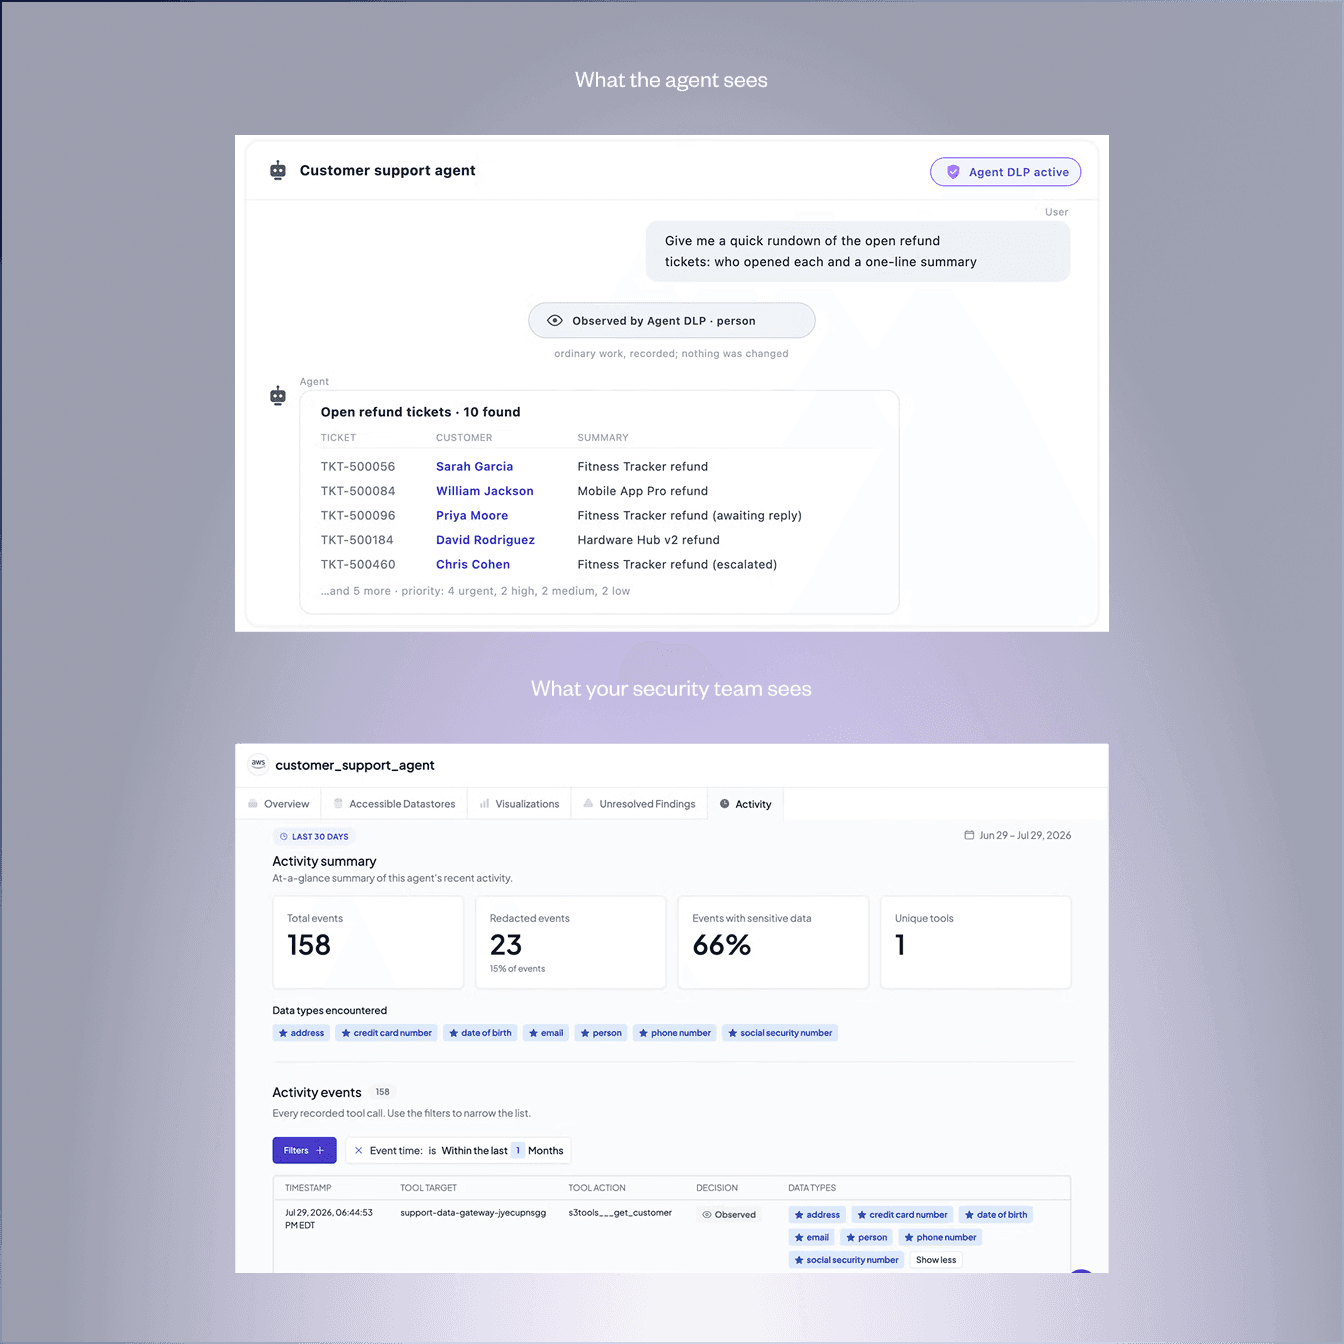
Record what agents touch and change nothing. The default with no policy set.
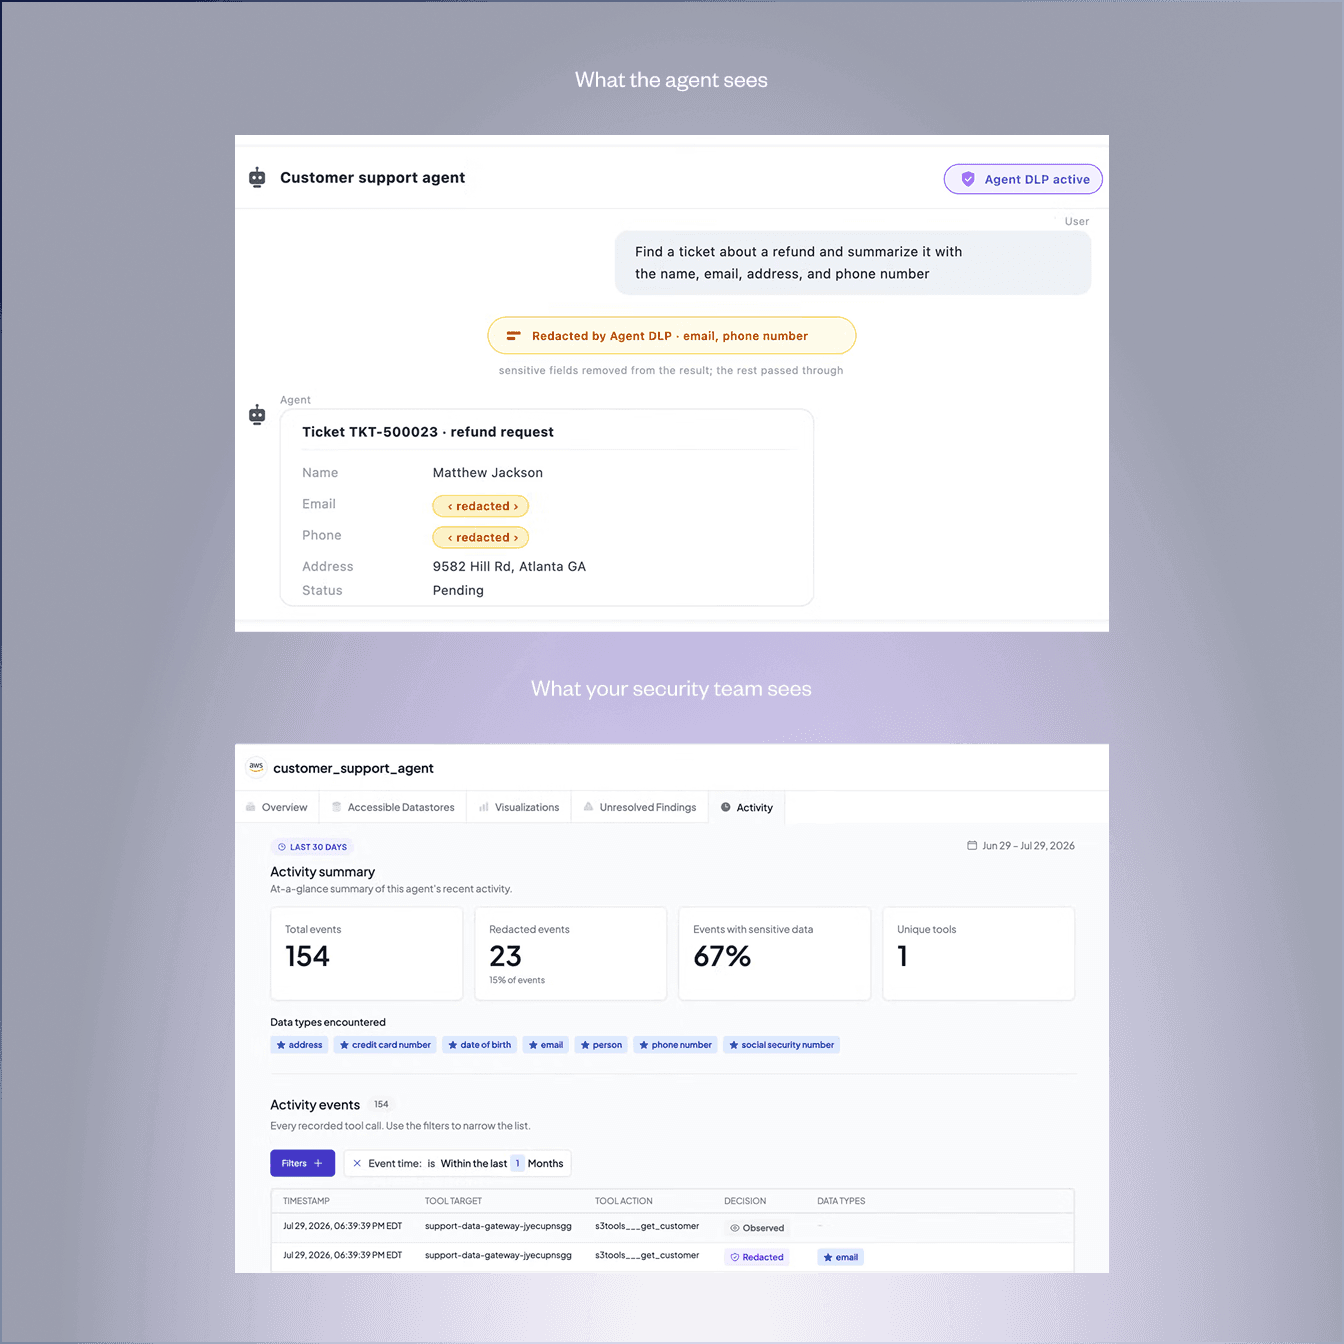
Strip sensitive values in place. The agent keeps working with the rest.
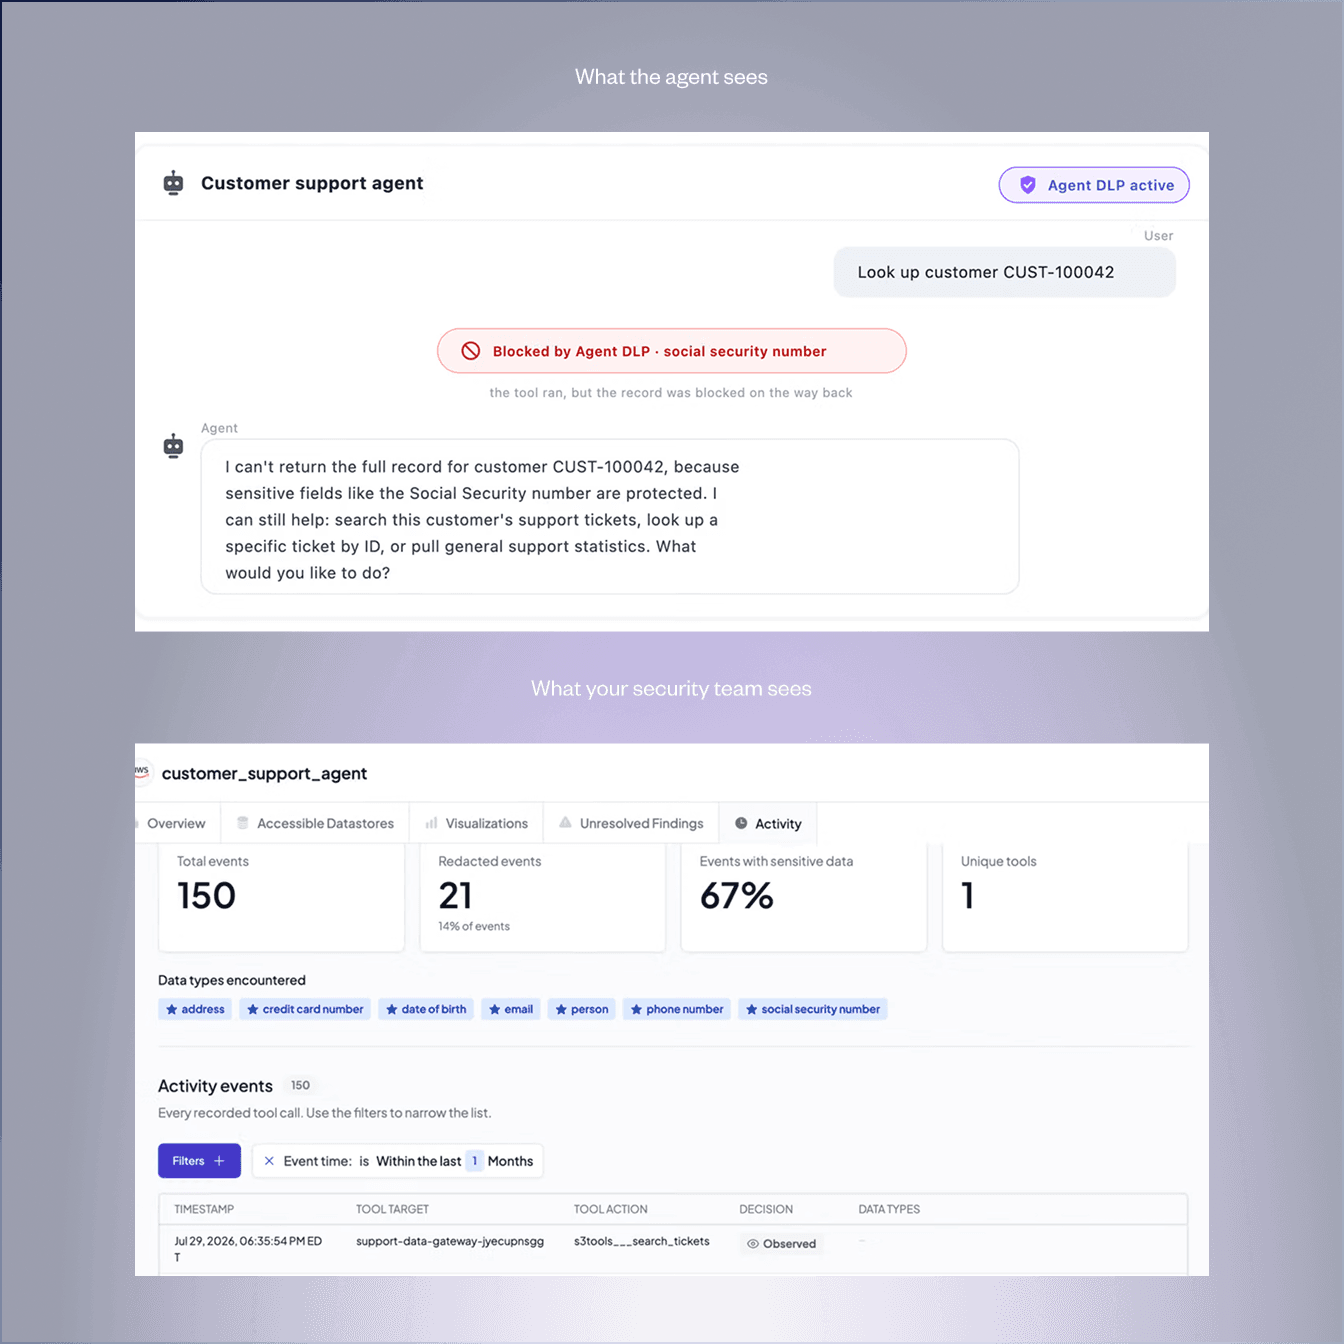
Stop the call. The action never runs and the agent gets a clear refusal.
Setup is two steps, and neither your agents nor your tools have to change.
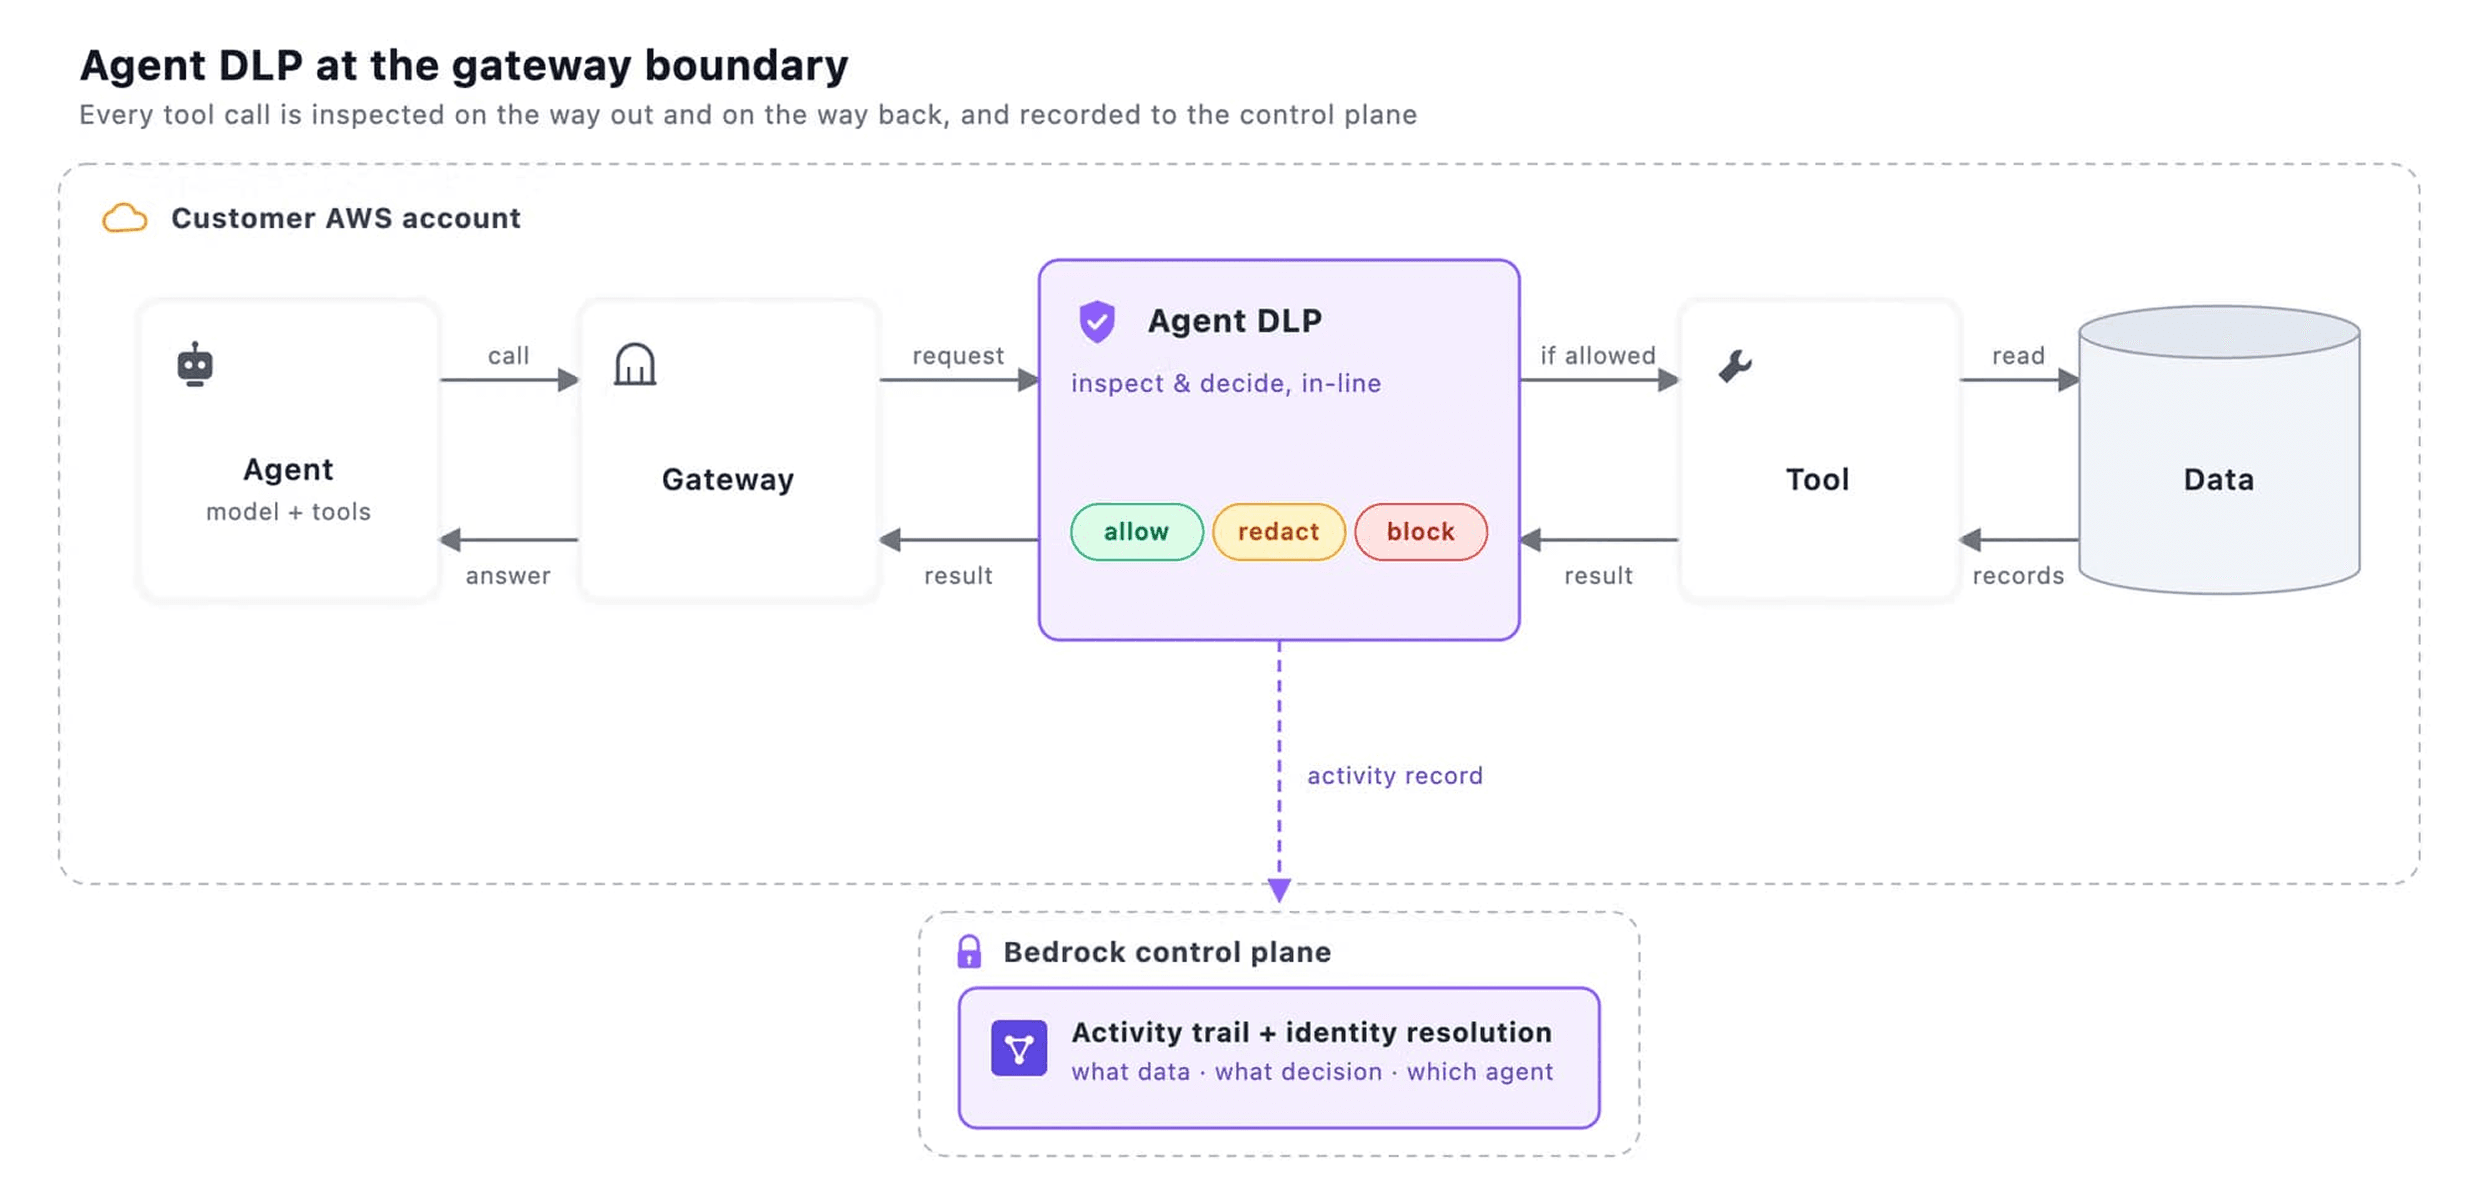
01
Drop the Bedrock Data interceptor Lambda into your own AWS account. It stays in your environment and reads only what it needs.
02
Set it as the request and response interceptor on your AgentCore gateway. Traffic starts flowing through inspection right away.
03
Start in observe mode to learn what agents touch, then tighten to redact or block by data type when you are ready.
ArgusAI already maps every agent and the data it can touch. Agent DLP enforces those same policies at runtime, so what you intend and what actually happens stay in step.
| Timestamp | Tool action | Decision | Data types |
|---|---|---|---|
| 06:42:44 | get_customer | Observed | SSN |
| 06:42:42 | search_tickets | Observed | credit card |
| 06:42:18 | get_customer | Observed | |
| 06:42:15 | get_customer | Observed | phone |
| 06:40:10 | search_tickets | Observed | address |


Every operation is allowed, redacted or blocked in real time, judged on the data, the identity and the policy together.

Native hooks into your existing agent infrastructure. No separate proxy to stand up, route around or maintain.

Machine learning reads messy free text; deterministic checks confirm structured identifiers like card numbers and government IDs.

It fails open, so inspection never becomes a new point of failure. Failures are logged and alertable, not silent.
EU AI Act · ISO/IEC 42001 · Colorado AI rules · California AI rules

With Bedrock Data, we can let agents work on the data that makes them valuable, because we control what they do with it the moment they act.
Governance at runtime is what turns AI from a risk conversation into a growth strategy.
Bruno Kurtic, CEO and co-founder, Bedrock Data
We use Bedrock Data at BCG to solve these problems for ourselves, so when we tell clients that command of their data comes first, we are speaking from experience.
Vladimir Lukic, Managing Director and Senior Partner, Boston Consulting Group